 By
TOKYO, Japan — A malware incident involving a third party handling customer information for Japanese entertainment company Daiichi Kosho has raised concerns about the security risks associated with outsourced data processing. The incident could affect approximately 8.7 million customer and employee records, according to disclosures reported in October 2026.
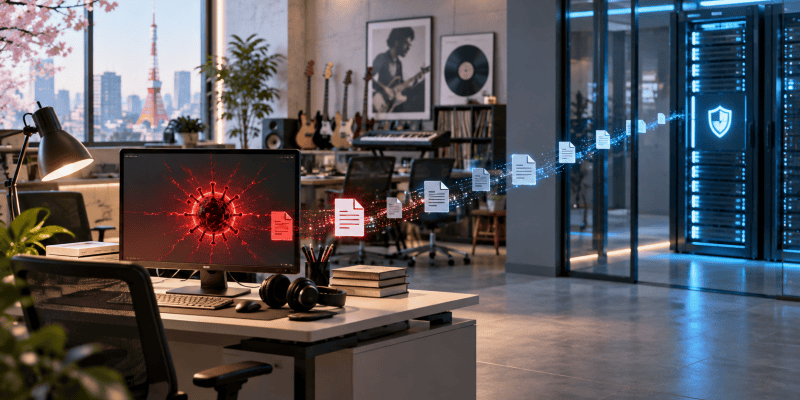
The malware was discovered on an employee’s computer at Nippon Columbia Group, a company that processes personal information on behalf of Daiichi Kosho. The incident highlights how cybersecurity weaknesses at external service providers can create risks for organizations even when their own internal systems have not been compromised.
Third Party Security Under Scrutiny
Daiichi Kosho reported that its contractor had identified malware on an employee’s device in early October. The affected computer was isolated, and an investigation was launched to determine the cause of the infection and whether personal information had been accessed or exposed.
The potentially affected records include information belonging to approximately 8.63 million customers and 93,000 employees. The data reportedly includes names, gender, dates of birth, email addresses and telephone numbers.
Daiichi Kosho has said its own systems were not compromised. The company also indicated that passwords were not included in the potentially affected information. At the time of the latest reports, investigators had not confirmed that the data had been stolen or published online.
Why the Incident Matters
The case demonstrates the importance of assessing cybersecurity beyond an organization’s own network. Businesses frequently rely on external providers for customer management, data processing, marketing, software and other operational services. If a supplier experiences a security incident, information entrusted to that supplier may become vulnerable.
Third party risk can be difficult to manage because organizations often have limited visibility into how vendors secure employee devices, control access to sensitive information and monitor suspicious activity. Security reviews that take place only during onboarding may also fail to identify weaknesses that emerge later.
For businesses handling large customer databases, vendor assessments, access restrictions, encryption and clear incident reporting procedures can help reduce exposure. Organizations should also understand which information each supplier needs and limit access to the minimum required for its work.
Potential Phishing Risks for Customers
Although passwords were not among the reported data categories, personal details such as names, birth dates, email addresses and phone numbers can be valuable to cybercriminals. When combined, these details may help attackers create convincing messages that impersonate a trusted company or service provider.
Customers should be cautious about unexpected emails, text messages and telephone calls requesting payments, account credentials or additional personal information. Messages that create urgency or direct recipients to unfamiliar websites deserve particular scrutiny.
The incident remains under investigation, and the possibility of exposure should not be treated as confirmation that information was stolen. Nevertheless, it reinforces a wider cybersecurity lesson: protecting customer data requires effective controls across the entire supplier network, not just within the organization that originally collected it.


Comments